September 2026 edition of BlueOrange Connections

Hi friend,
The past couple of years at CloudWave have been exciting for several reasons, but I’m probably most excited about the acquisitions of Sensato and BlueOrange Compliance. We added team members who were culturally compatible and whose capabilities are critical to the industry we serve. As Tim Quigley noted over a year ago, “CloudWave is redefining healthcare cybersecurity resilience by seamlessly integrating IT infrastructure, cloud security, and managed threat protection to provide a unique and valuable way to secure your hospital…Security-IT convergence is not just about connecting security and IT; it transforms how they work together to create a stronger, more resilient organization.” We still believe this to be true, and even more so given the impact AI is having on cybersecurity and the healthcare industry.
While we’ve emphasized these acquisitions and our cybersecurity capabilities frequently in this forum and others, I want to assure you that we remain equally committed to the fundamental services that define CloudWave’s DNA: hosting, disaster recovery, backup-as-a-service, edge, and on-premises infrastructure solutions. Underpinning all of these services is a mantra of meeting our customers where they are. In practice, that means we won’t push private cloud hosting over a customer’s desire to purchase and manage
on-premises infrastructure. We will certainly provide our advice, expertise, and experience to help customers evaluate alternatives, but we understand that many factors influence what constitutes the “right” decision for any given customer. Those factors might include concerns about internet connectivity, the need for a capex solution versus an operating expense-based solution, or how an organization chooses to manage risk. We don’t have an agenda to force hosting, private cloud, or any solution on a customer (despite our name, yes- I know!). We hope that offering customers alternatives and maintaining the ability to resell hardware and perform on-site implementations differentiates CloudWave from traditional managed service providers and value-added resellers.
Our commitment to these managed services and on-premises capabilities is also reflected in the investments we continue to make in the technology, tools, people, and operating models behind them. These investments are not simply about introducing new technology; they help organizations maintain highly available, performant, and secure environments while navigating market dynamics that continue to pressure IT budgets and operating models. These pressures include rising hardware and infrastructure costs, increasing software and licensing expenses, greater regulatory and compliance requirements, evolving cyber insurance expectations, and the ongoing challenge of attracting and retaining specialized technical talent. At the same time, organizations are being asked to consistently reduce the cost and complexity of IT and security operations. Apparently, “do more with less” wasn’t ambitious enough!
A few examples include our transition to Nutanix, which provides a modern infrastructure platform while helping mitigate the rising costs associated with traditional virtualization technologies; our investment in ScienceLogic, which gives our teams deeper monitoring, observability, event correlation, and capacity insight to help identify issues earlier and make more informed infrastructure decisions; and the continued evolution of our Customer Partnership Management program, which creates greater accountability and more proactive engagement around service health, customer priorities, optimization opportunities, and long-term planning.
We are also expanding the use of automation and operational standardization across our services to reduce repetitive manual work, improve response times, and allow our technical teams to focus their expertise on the items that create the greatest value for customers.
Taken together, these investments are designed to create greater operational leverage. Better visibility can help identify capacity and performance issues before they become problems. Automation can reduce the effort required to operate increasingly complex environments. Modern infrastructure platforms can help control licensing and technology costs. Stronger customer engagement can also help identify opportunities to optimize an environment before additional investment is required.
Ultimately, our goal is to help customers address what can often feel like competing priorities: keeping critical systems available, performant, resilient, and secure while also lowering the overall cost of IT and security. Our investments are tangible examples of how we are building our services around achieving both. Just as importantly, our role is not to prescribe a single technology strategy, but to provide the flexibility, expertise, and operational support to help each customer make the right decisions for their organization. Whether that means private cloud, edge, on-premises infrastructure, managed security, or a combination of approaches, our commitment remains the same: to meet customers where they are and help them operate more reliably, securely, and efficiently.
Erik Littlejohn
President and CEO, CloudWave
John DiMaggio on AI Panel at MEDITECH LIVE 26
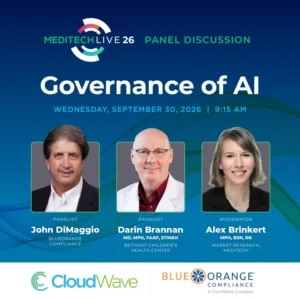
As Managing Director & Co-Founder of BlueOrange Compliance, John DiMaggio will join the Governance of AI panel on Wednesday, September 30, at MEDITECH LIVE26 where he will share strategies for balancing innovation with privacy, security, and patient trust, along with Darin Brannan, MD, MPH, FAAP, DTM&H, and Alex Brinkert, Chief of Clinical Innovation from Bethany Children’s Health Center.
Register for MEDITECH LIVE→
 WHITEPAPER: AI Primer for the Board of a Hospital or Health System
With AI now readily accessible in clinical and administrative settings, it’s critical for healthcare leaders to know about AI risk, governance, and oversight. Read more→
 Don’t wait, schedule your Security Risk Assessment today
Don’t wait until compliance deadlines or cyber incidents put your healthcare enterprise at risk. Partner with BlueOrange Compliance for a HIPAA Security Risk Assessment that strengthens both compliance and patient safety. Learn more →
Consider Penetration Testing
You may be armed with firewalls, antivirus, and MFA, but are you confident that what you’ve done could prevent today’s sophisticated attackers from finding their way in? Are you able to document that your security controls are doing their job? CloudWave and BlueOrange’s Penetration Testing is a solid start. It can also provide actionable insight you can use to close security gaps, strengthen compliance, and protect patient care.
Learn more →
Become a Cybersecurity Insider
We’re excited to invite you to join our Cybersecurity Insider Program (CIP) — your exclusive gateway to the latest healthcare cybersecurity insights and resources.
Register today to get these exclusive benefits:
- On-Demand Learning Library
- Exclusive Member Offers
- Early Access to Specialized Content
- CIP Roundtables, Webinars, & Events

Events & Webinars
LeadingAge Annual Meeting | October 25 – 28 | Philadelphia, PA | Convention Center, Learn more
Product & Platform Updates
- Security Risk Assessments
As part of our ongoing effort to keep the Security Risk Assessment aligned with emerging risks, future SRA engagements will include an AI readiness component. This is intended to help organizations understand where AI is being used, identify potential governance gaps, and ensure AI-related risks are being managed appropriately. - BlueOrange Compliance Elevates Cybersecurity with NIST CSF 2.0
Healthcare organizations continue to face rising cyber threats, tighter regulatory scrutiny, and increasing operational pressure. In this environment, a strong, future-ready cybersecurity and compliance posture is essential. That’s why BlueOrange Compliance is proud to announce our transition to the NIST Cybersecurity Framework (CSF) 2.0, fully integrated with NIST SP 800-53 Rev. 5 and NIST SP 800-66 Rev. 2. This upgrade replaces our previous assessment approach rooted in 800-53 Rev. 4 and 800-66 Rev. 1, offering a more comprehensive, modernized, and aligned path to security and HIPAA compliance. Read More → - EDR Powered by SentinelOne: Simplify endpoint protection and visibility. Read More →
Resources & Insights
- Recent Blogs – Expert perspectives on data protection, cybersecurity, compliance,and cloud strategy.
- Endpoint Detection & Response Digital Hub – Access resource guides, webinar recordings, blogs, and best practices.
- Tell Your Story – Help other healthcare organizations by sharing how you’ve overcome your technical and security challenges. Email Us →
Thank you for being part of our BlueOrange Compliance customer community. We’re proud to support your mission to keep healthcare safe, connected, and resilient.
Stay tuned for next month’s issue!
– The BlueOrange Team